
Framework / ISO/IEC 42001
Map your AI governance evidence to ISO/IEC 42001.
ISO/IEC 42001 provides a structure for an AI management system. Fencia maps selected requirements to related EU AI Act and GDPR work, so you can link evidence, identify open questions and record a reviewer’s decision in one place.
This is a governance mapping. Fencia does not analyze uploaded documents against ISO/IEC 42001, conduct an ISO audit or grant certification.
 Governance map / Crosswalk
 Live product
Voluntary standards in the same view
ISO/IEC 42001, mapped from the AI governance work you already do
Adopt the standard and its clauses move with the evidence you link and the decisions you record: AI policy gaps, reviewed findings, AI literacy sessions.
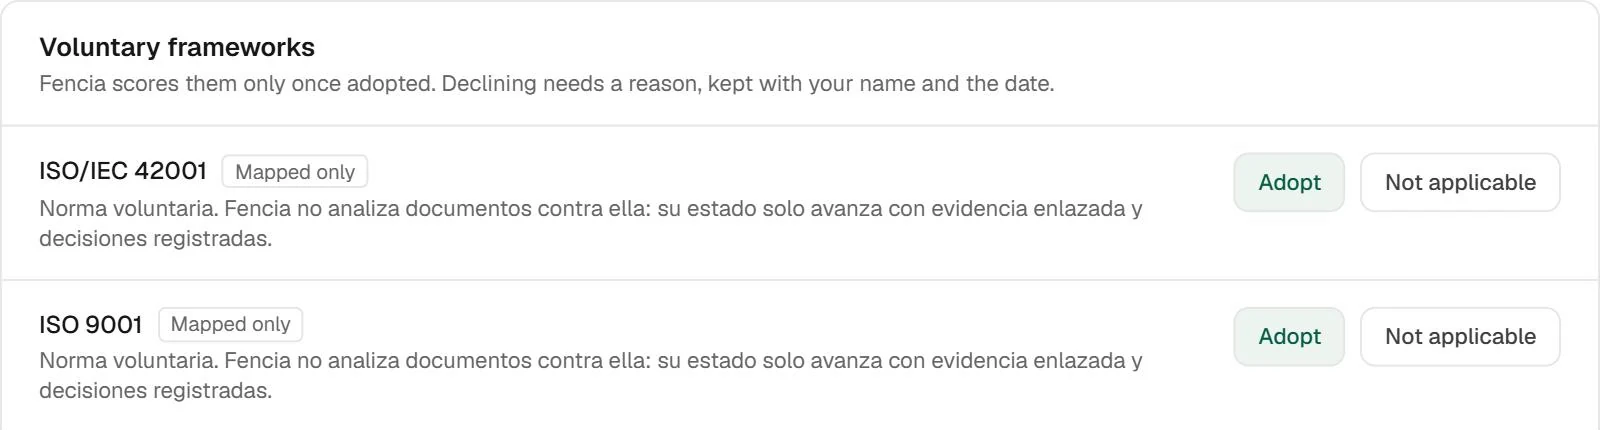
Adopt it when it is a goal
Voluntary standards count in readiness only once you adopt them. Declining one needs a reason, kept with your name and the date, so the decision can be explained later.
Fencia does not analyse documents against ISO/IEC 42001
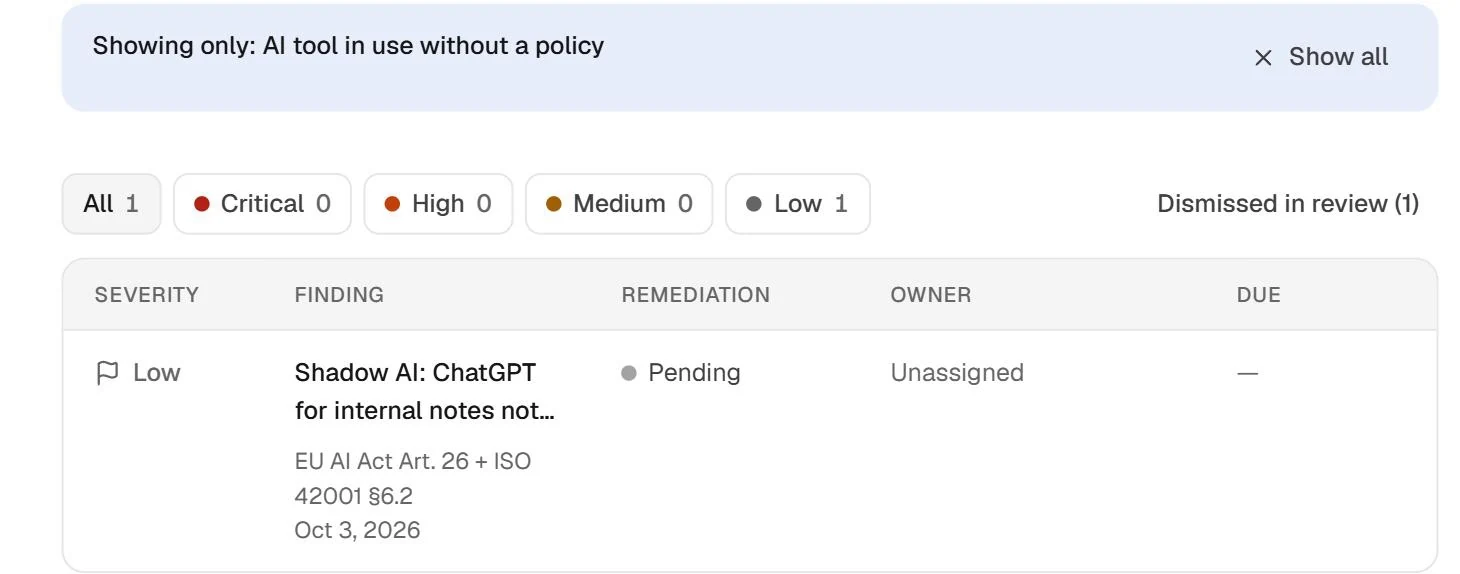
One finding, both frameworks
A tool in use that your AI policy does not cover maps to Article 26 of the EU AI Act and clause 6.2 of ISO/IEC 42001, so the same fix moves both. AI literacy sessions likewise propose evidence for clause 7.2.
Related evidence is a prompt for review, never automatic proof
Real Fencia screens from a test workspace. Names and data are fictional.
The exact product boundary
A map for your review, not an ISO audit.
The Fencia register (2026-10-15.1) maps selected ISO/IEC 42001 requirements using the standard’s structure. Its status advances through linked evidence and recorded decisions, not through a document scan against the standard.
Read ISO’s overview of the standard- Mapped requirements
- Fencia shows selected requirements and curated relationships to EU AI Act or GDPR work. The map does not reproduce the licensed standard text.
- Evidence and decisions
- A reviewer can link evidence to a mapped requirement and record a decision about its relevance or sufficiency.
- Document scanning
- Uploaded documents are not analyzed against ISO/IEC 42001. Any EU AI Act or GDPR scan result remains within that framework’s own supported scope.
- Certification
- Fencia does not issue an ISO/IEC 42001 certificate or replace an independent certification audit.
ISO/IEC 42001 questions before you start
A map tells you where to look; an assessment asks whether the evidence is enough. Certification needs an independent process outside Fencia.
Will Fencia certify us?
No. Fencia does not issue an ISO/IEC 42001 certificate or replace an independent certification audit.
How does a clause move forward?
Through evidence you link and decisions you record. A document scan for the EU AI Act or GDPR stays within that framework's scope.
Does Fencia include the text of the standard?
No. It follows the standard's clause structure without reproducing its licensed text.
Which other voluntary standards can I adopt?
ISO 9001, HIPAA, SOC 2 and PCI DSS are mapped the same way: they count only once adopted, and declining one needs a reason.
Reuse the work you already did
Adopt ISO/IEC 42001 in your workspace and see which clauses your current evidence and decisions already speak to.